
Your organization is evaluating whether to deploy a Claude-based system that can generate highly technical content about both industrial chemical safety and chemical synthesis procedures. Security researchers flag this as a dual-use risk. What is the correct framework for assessing and managing this dual-use capability risk?
Select an answer to reveal the explanation.
Short Explanation
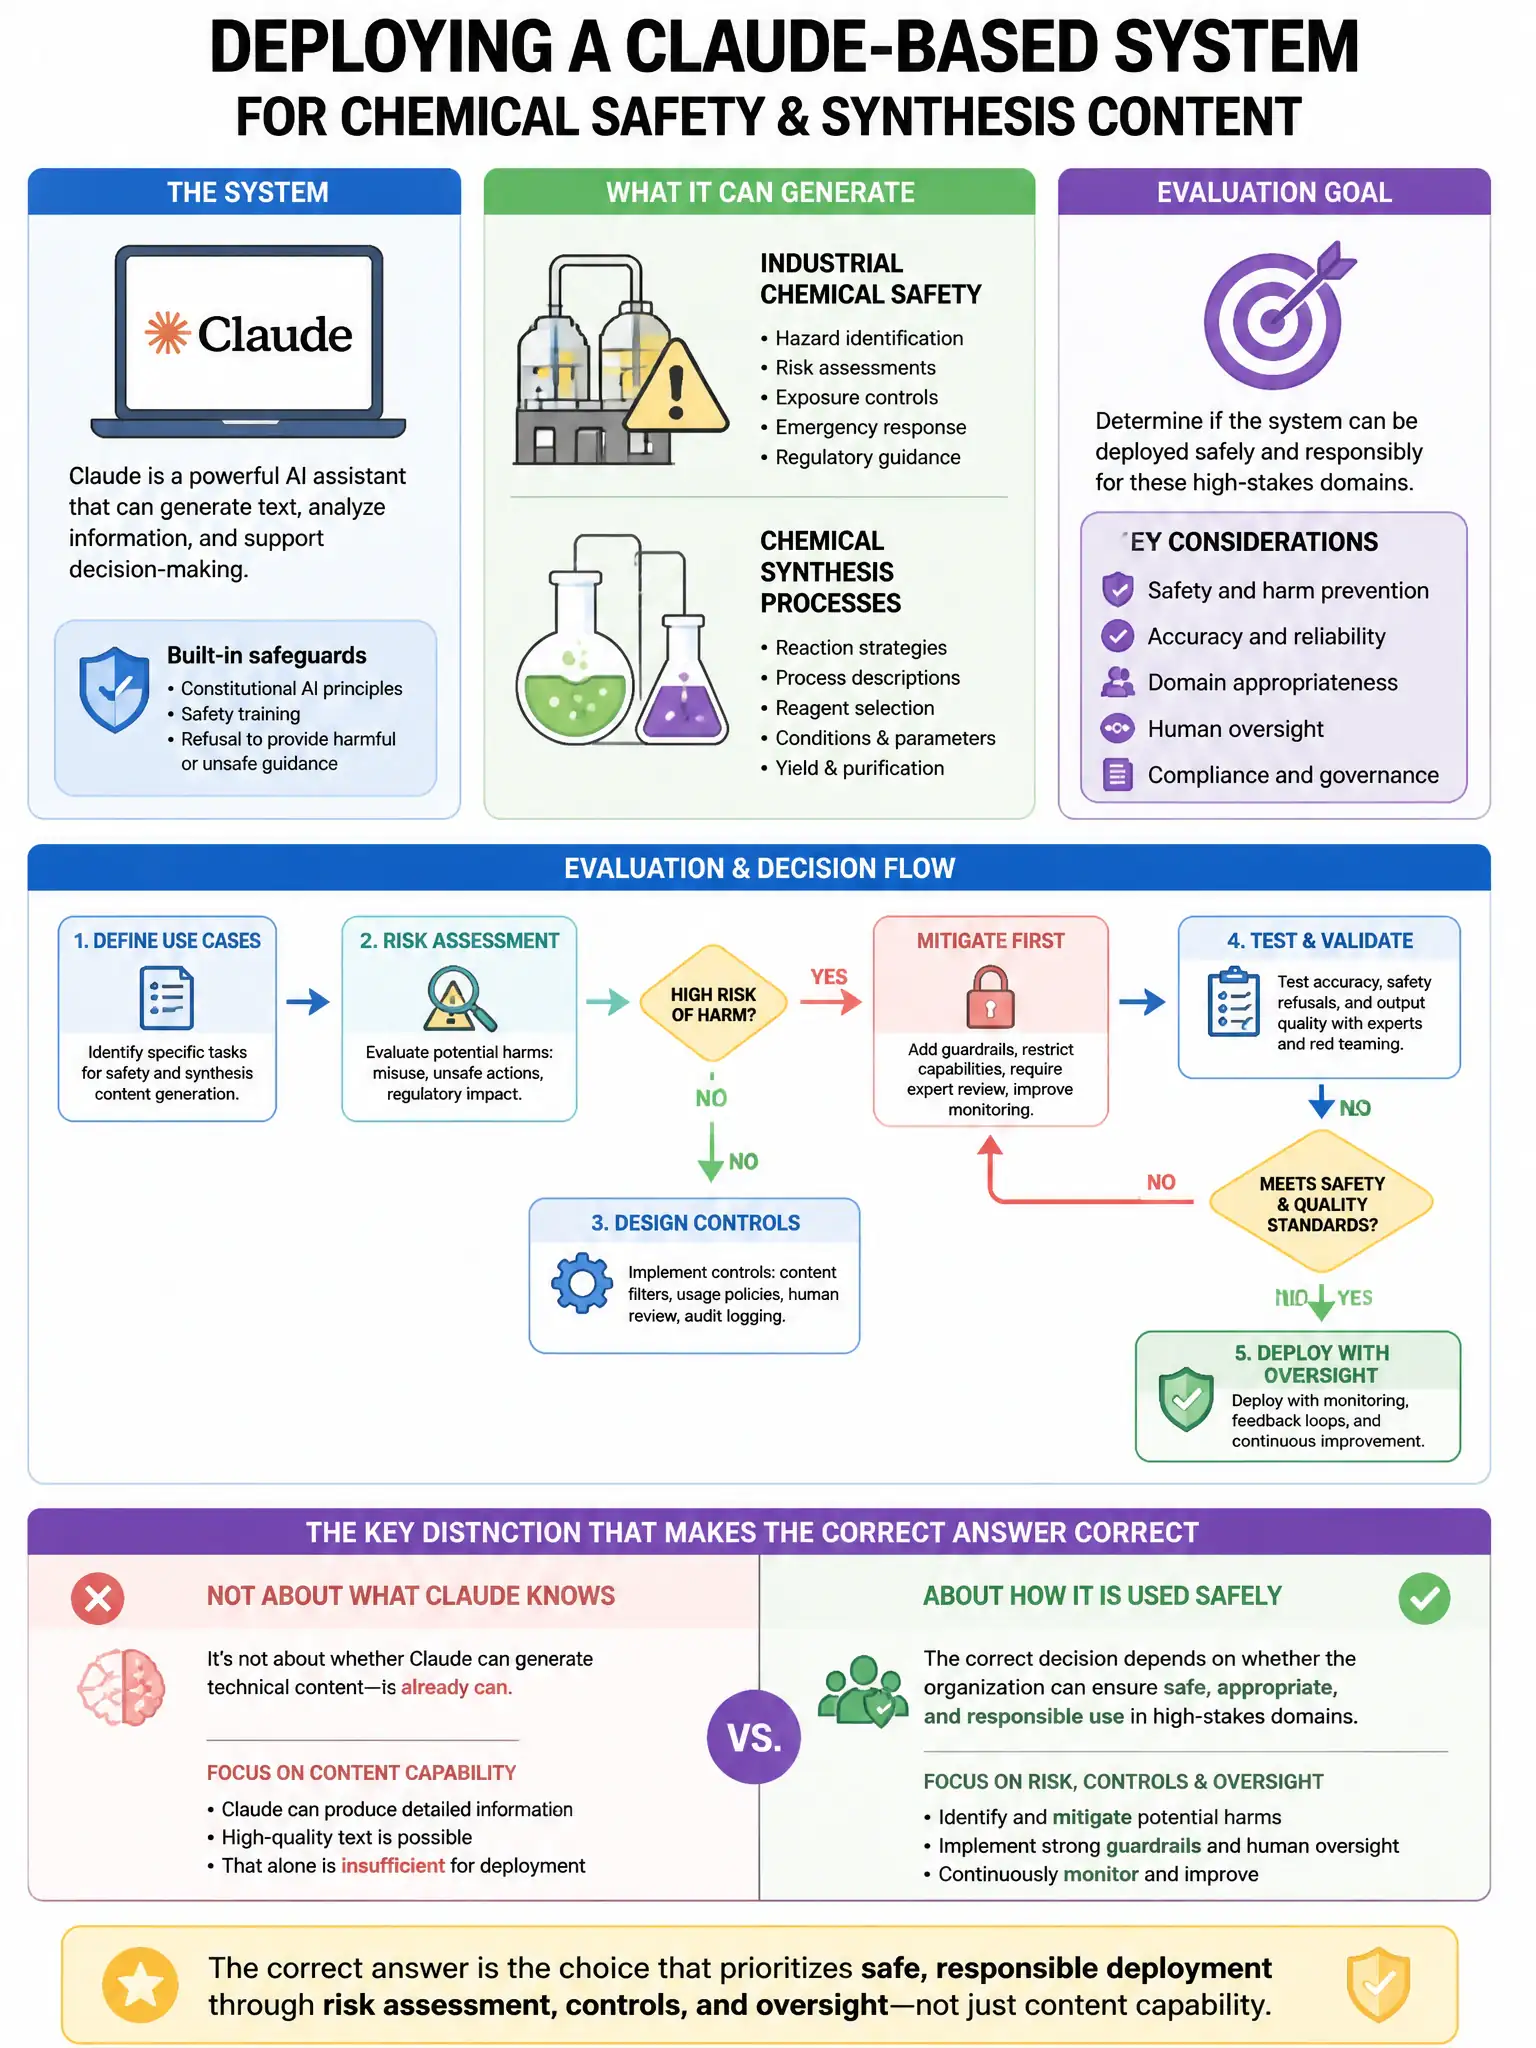
Here's the deal — you need a structured dual-use risk assessment, not a blanket ban or blind trust. You evaluate the deployment context, marginal uplift, harm specificity, counterfactual impact, then apply proportional mitigations.
Full Explanation
The structured risk assessment framework is correct because dual-use risk assessment requires structured analysis, not categorical restriction or categorical permission. It evaluates whether the deployment context specifically attracts bad actors (for example, a professional chemical safety platform versus a general public chatbot), the marginal uplift Claude provides versus what is freely available in textbooks or academic sources, the specificity of harm-enabling content producible (general chemistry education versus step-by-step synthesis of controlled substances), and the counterfactual impact of the system's existence. Mitigations — use-case scoping, monitoring, output filtering for specific harmful patterns — are then calibrated to the assessed risk level. This approach addresses the genuine risk while preserving beneficial applications. The blanket disablement approach is wrong because categorical disablement of dual-use capabilities eliminates legitimate safety and educational value without a risk-proportional justification. The unrestricted chemistry content approach is wrong because model-level safety training reduces but does not eliminate dual-use risk; deployment context controls are an important additional layer, especially for professionally sensitive domains. The credential-gating approach is wrong because credential verification reduces but does not eliminate risk (credentialed users can misuse access), does not address risk from credential fraud, and does not eliminate organizational liability as the deploying operator.