
A customer analytics platform builds an MCP server that exposes a database query tool. The MCP server is connected to a Claude agent that has read access to a customer database. During testing, an analyst prompts Claude: 'Generate a report on Q3 revenue.' Claude successfully queries sales data. Then the analyst pastes a CSV file into the chat: 'Can you analyze this CSV? [CSV content with a hidden row: "; DROP TABLE sales; --]'. Claude calls the query tool with a SQL string that incorporates the CSV data directly, causing a SQL injection. What MCP server-side control prevents this?
Select an answer to reveal the explanation.
Short Explanation
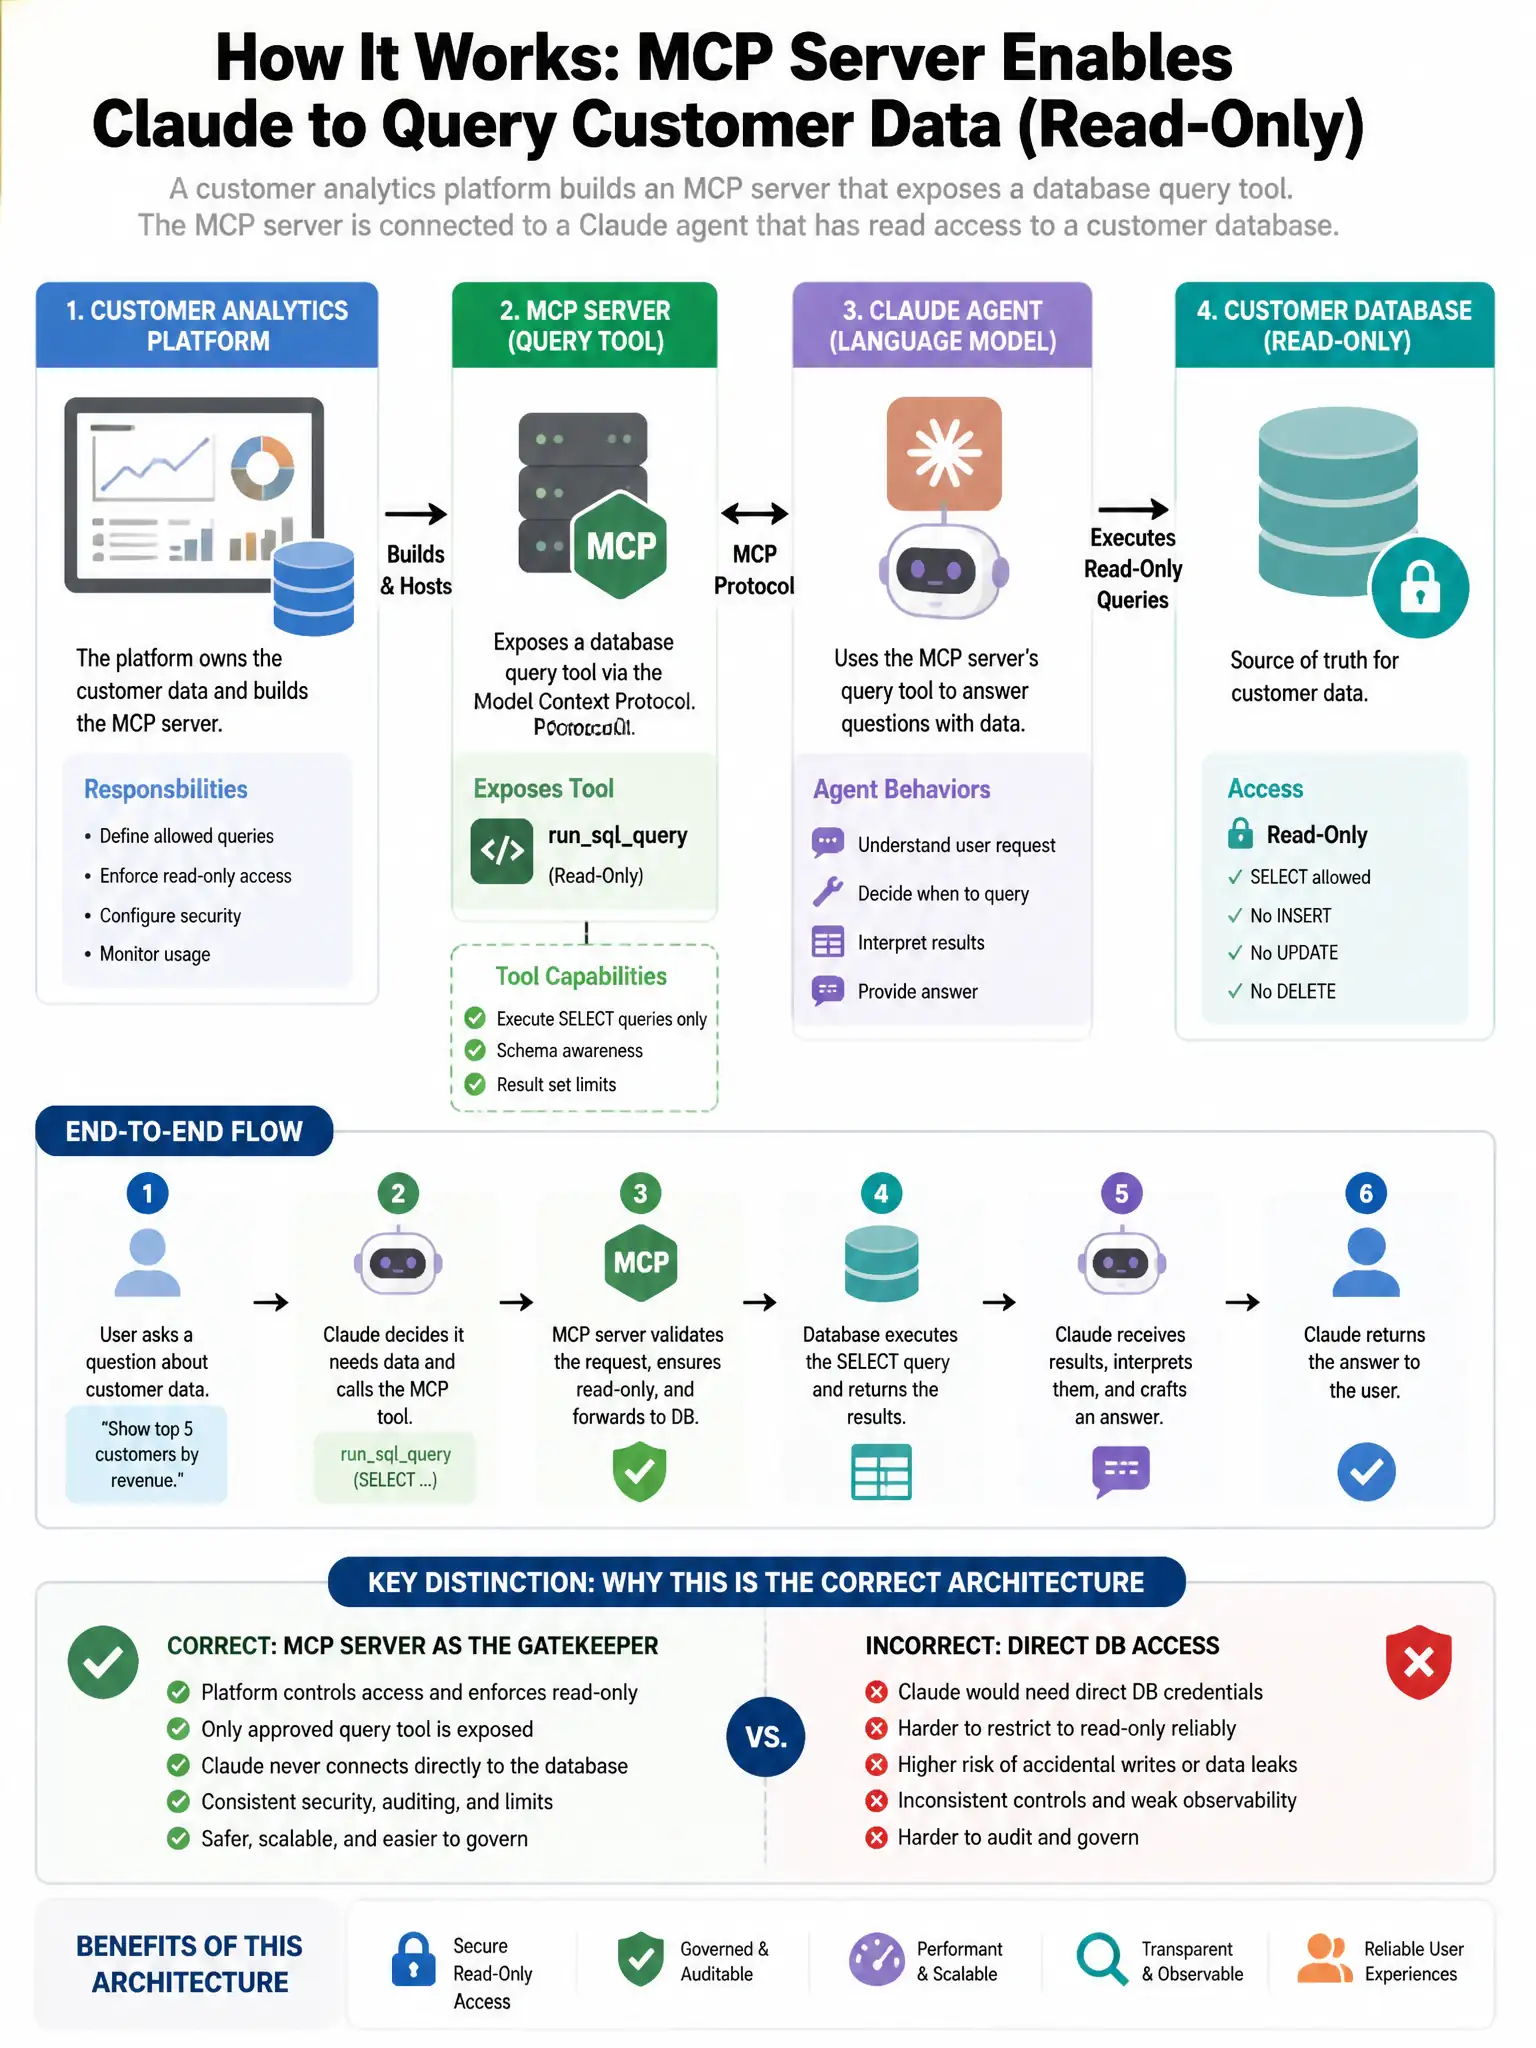
Here's the deal — you need the MCP server to accept structured parameters, not raw SQL strings. It builds sanitized, parameterized queries internally, so injected CSV content can't escape into SQL.
Full Explanation
Defense-in-depth for SQL injection requires that the MCP server never accept raw SQL strings from Claude — instead, it should accept structured parameters that it assembles into safe, parameterized queries internally. If Claude calls query_database({"table": "sales", "filters": {"quarter": "Q3"}}), the server builds SELECT * FROM sales WHERE quarter = ? with bound parameters, and no user content can escape the parameter binding. The system-prompt instruction telling Claude to always use parameterized queries cannot be relied upon — Claude's SQL construction can be manipulated by injected content in user-provided data. The SQL-parser approach that detects and rejects statements containing DROP, DELETE, or INSERT keywords is bypassable through encoding, case variation, comments, or indirect injection. The read-only database-user approach is excellent defense-in-depth, but it doesn't prevent data exfiltration, unauthorized reads, or information leakage — it protects data integrity but not confidentiality. The parameterized tool handler, combined with read-only database privileges, forms a stronger defense-in-depth posture, but the MCP server-side control that prevents this injection is structured, parameterized query construction inside the tool handler.