
A historic carillon desk wants a simple you should turn this on checklist for cost, security, and service limits on the AI account. A colleague suggests CloudTrail, Config, or an audit-manager product. Which service is that guidance role?
Select an answer to reveal the explanation.
Short Explanation
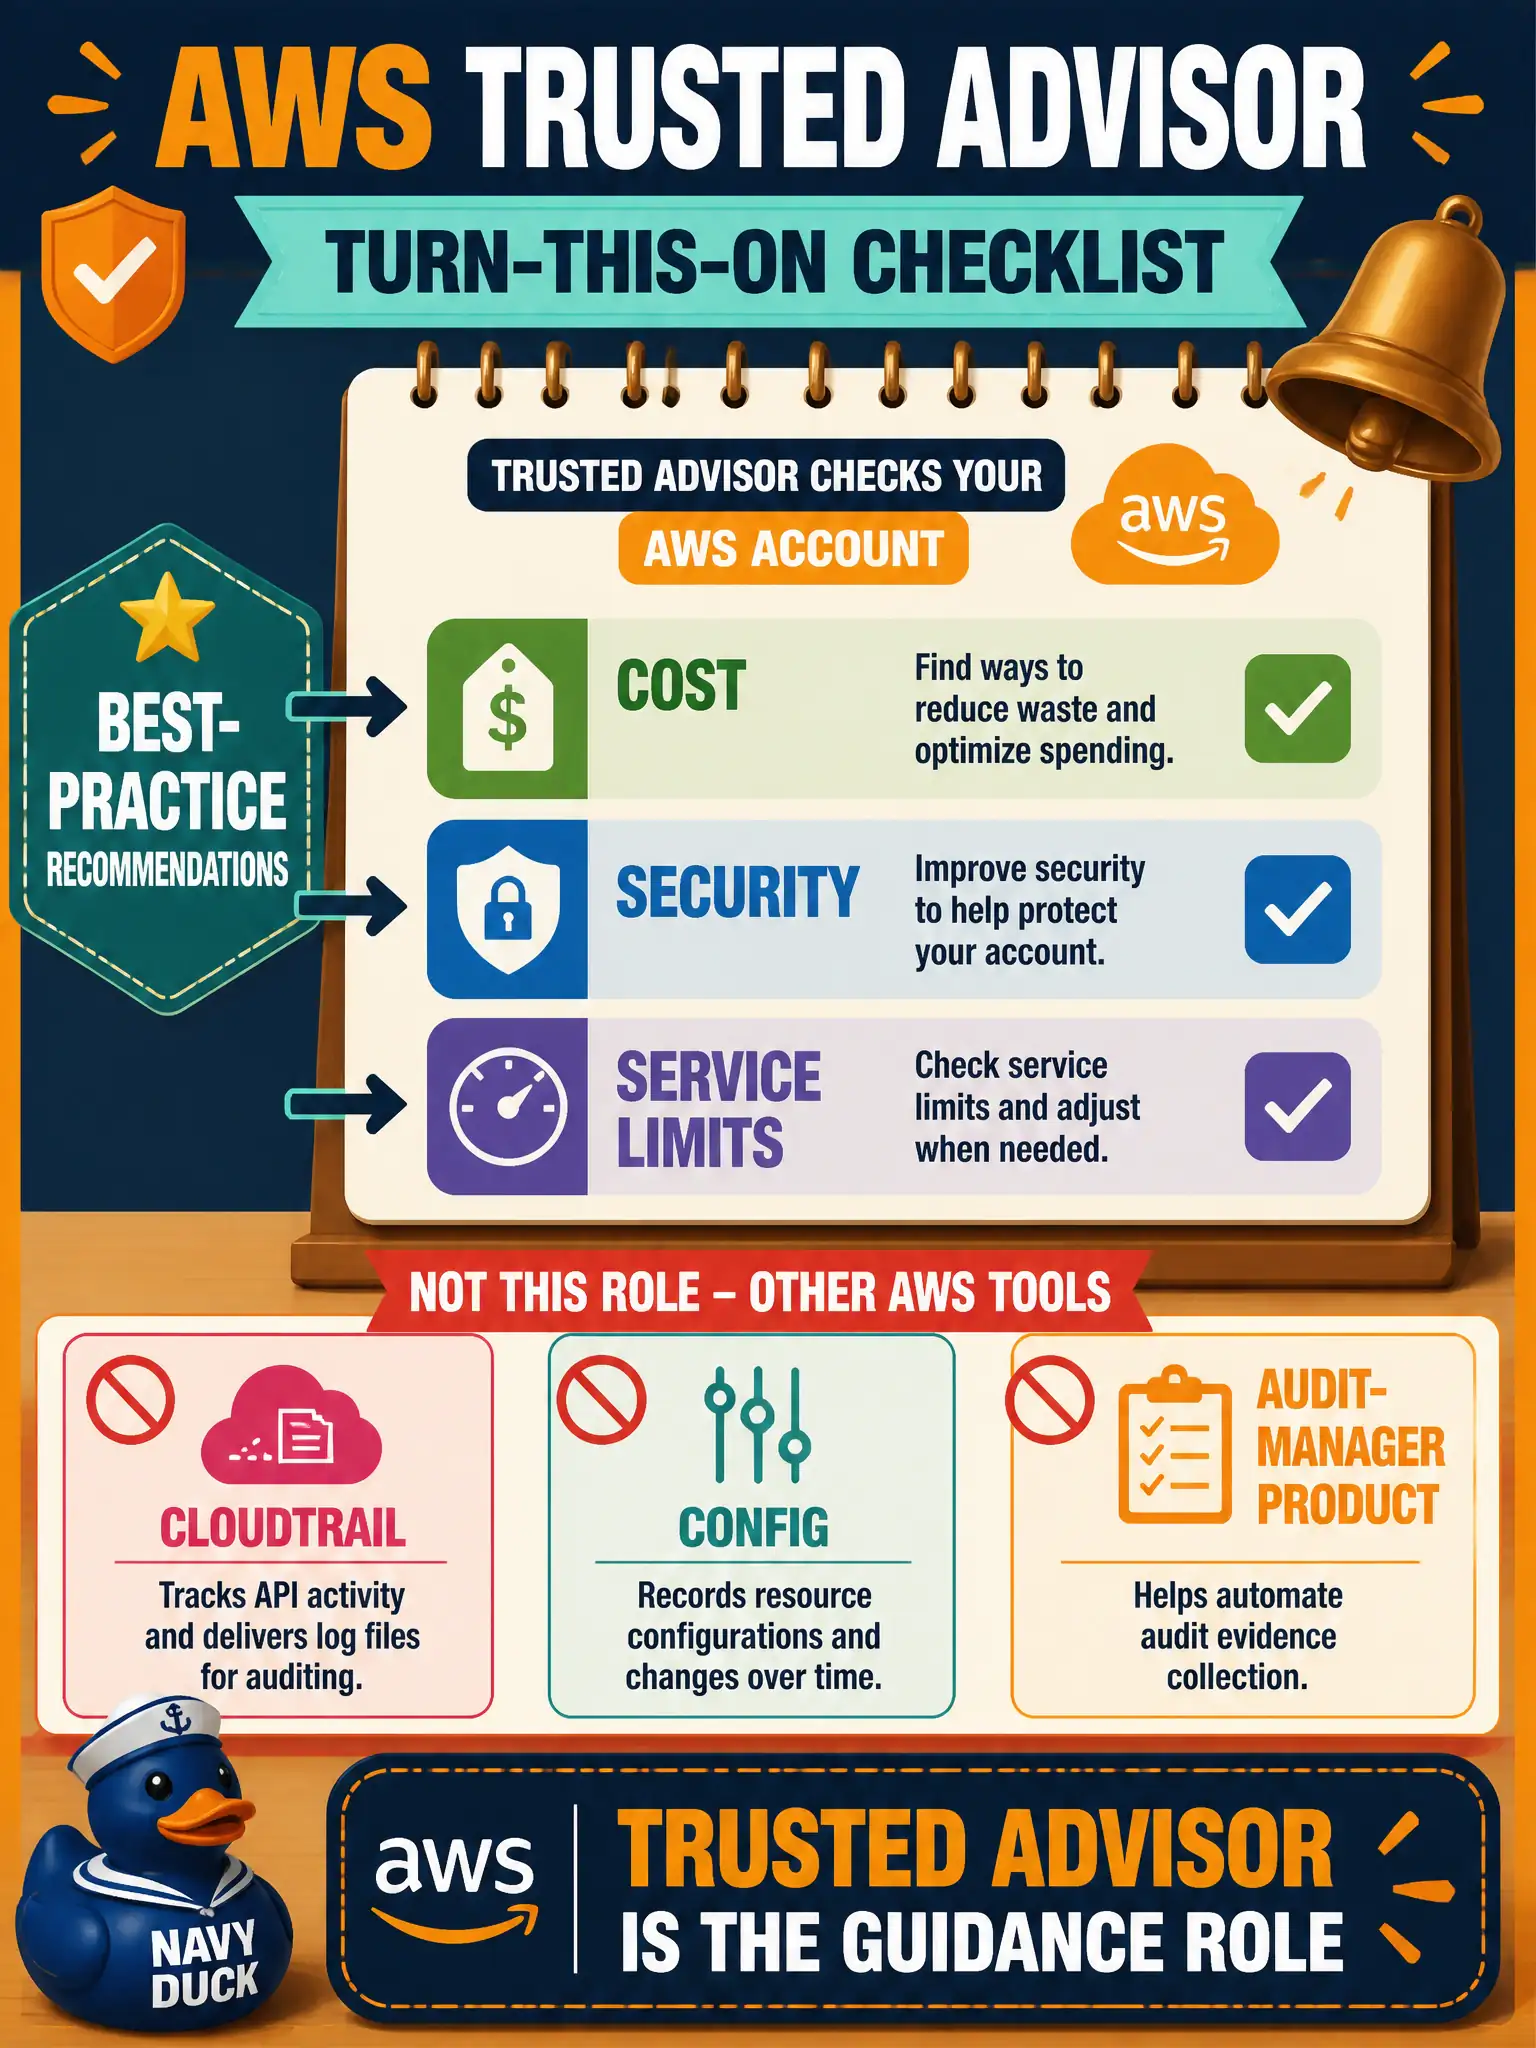
Think of a simple you-should-turn-this-on checklist for cost, security, and limits. That guidance role is AWS Trusted Advisor. CloudTrail, Config, and an audit-workpaper tool are different jobs.
Full Explanation
The historic carillon desk wants a simple you-should-turn-this-on checklist covering cost, security, and service limits on the AI account. That guidance role is AWS Trusted Advisor: curated best-practice recommendations across those categories, distinct from deep audit workpapers or configuration history. Use it to spot missing encryption, open access patterns, service-limit risk, and cost waste, then turn recommendations into tickets the AI team can close.
CloudTrail fails by concept for this role: it is a who-did-what trail of API activity, not a should-turn-this-on recommendations list. AWS Config fails as a substitute for that checklist role: it watches and evaluates configuration against rules you define; it is not the same as Trusted Advisor’s curated recommendations catalog for cost, security, and limits. An audit-workpaper tool fails because collecting evidence for audits is not the same service as proactive best-practice guidance for what to enable.
Exam caveat: Trusted Advisor recommendations vary by support tier; some checks require Business or Enterprise support—know what your account can see before promising coverage to leadership. Operational check: open Trusted Advisor for the AI account, review security and limits findings related to buckets and quotas, create remediation tickets for high-risk items, and re-check after changes to confirm the checklist items clear.