
A temporary guest VLAN resource must leave a civic center switch that Terraform owns. How should deprovisioning be done in the Terraform workflow?
Select an answer to reveal the explanation.
Short Explanation
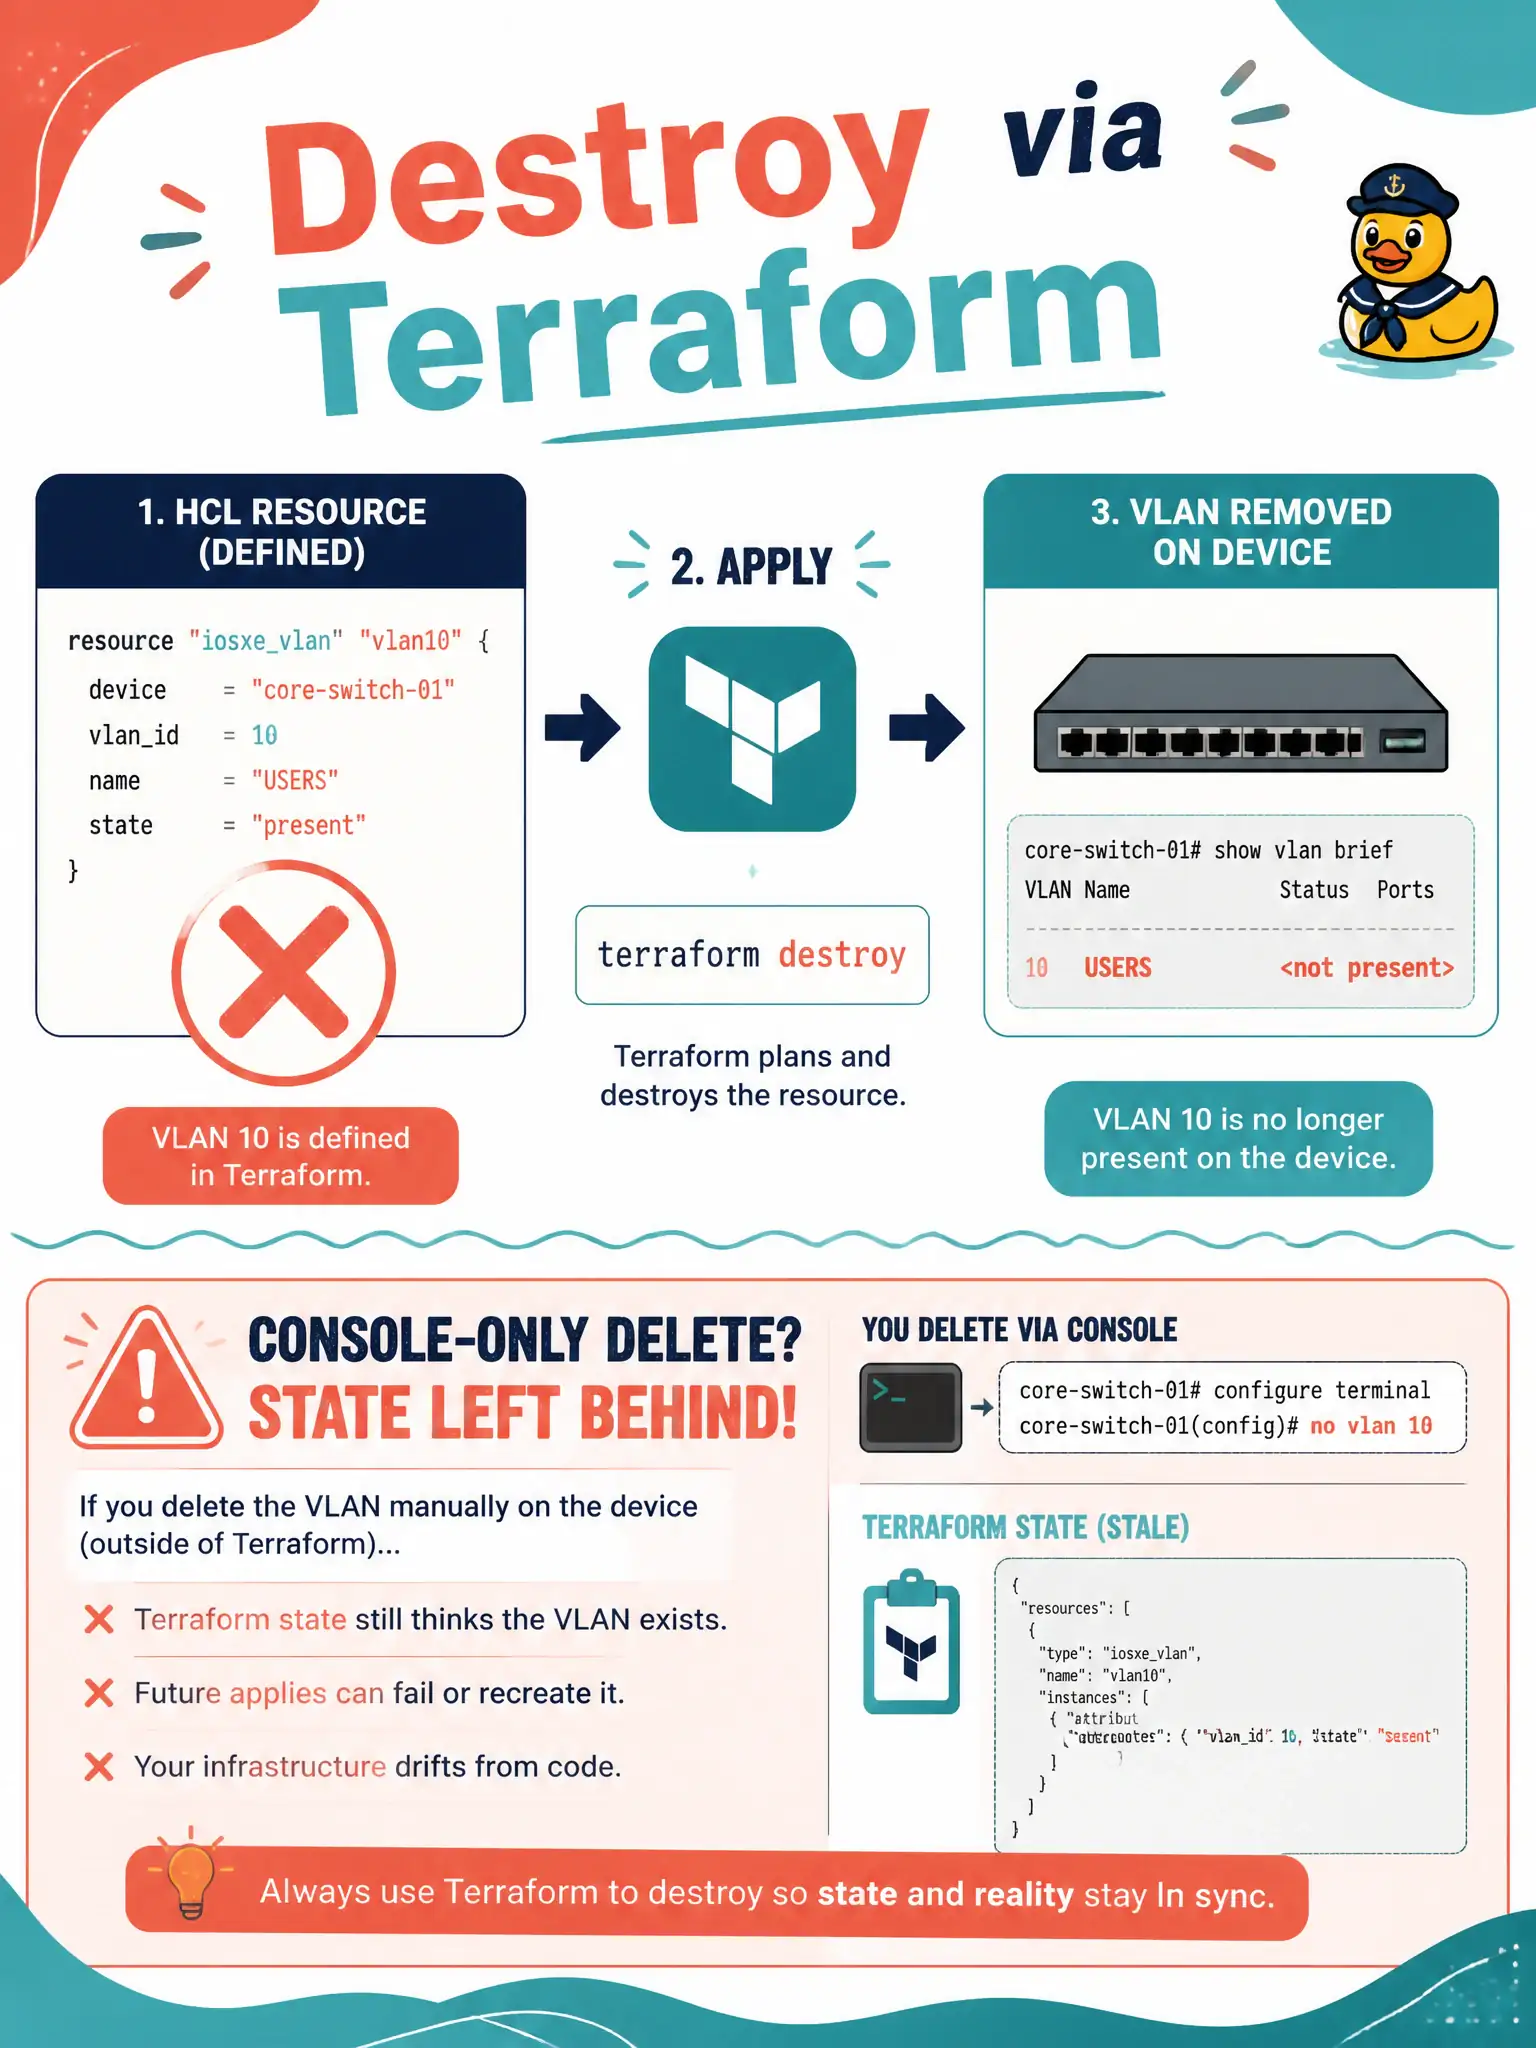
Take the shelf off the blueprint and apply—Terraform clears what it owned. A console “no vlan” leaves state lying about reality.
Full Explanation
Terraform deprovisions by removing or commenting out the resource from HCL and applying so Terraform destroys what it owns and updates state accordingly. For a temporary guest VLAN on a civic center switch, that is the honest workflow: desired configuration no longer includes the VLAN, plan shows a destroy, and apply removes it cleanly. Console deletes that leave HCL and state untouched teach Terraform the wrong story about ownership.
Running no vlan on the console while leaving the resource in HCL and state creates drift—the next plan wants the VLAN back because desire still declares it. Deleting only the state entry while keeping the HCL resource forever makes the next apply try to create again while humans believe the VLAN is gone. Disabling SSH so Terraform cannot see the VLAN breaks management without completing real deprovisioning.
Exam caveat: dependent resources such as SVIs, ACLs, or DHCP helpers may block destroy—remove or reorder dependents in HCL first. Always review plan for destroy before the production maintenance window on civic switches.
Operational check: remove the guest VLAN resource from HCL, confirm plan lists a destroy, apply, and verify the VLAN is absent both on-box and in terraform state list.