
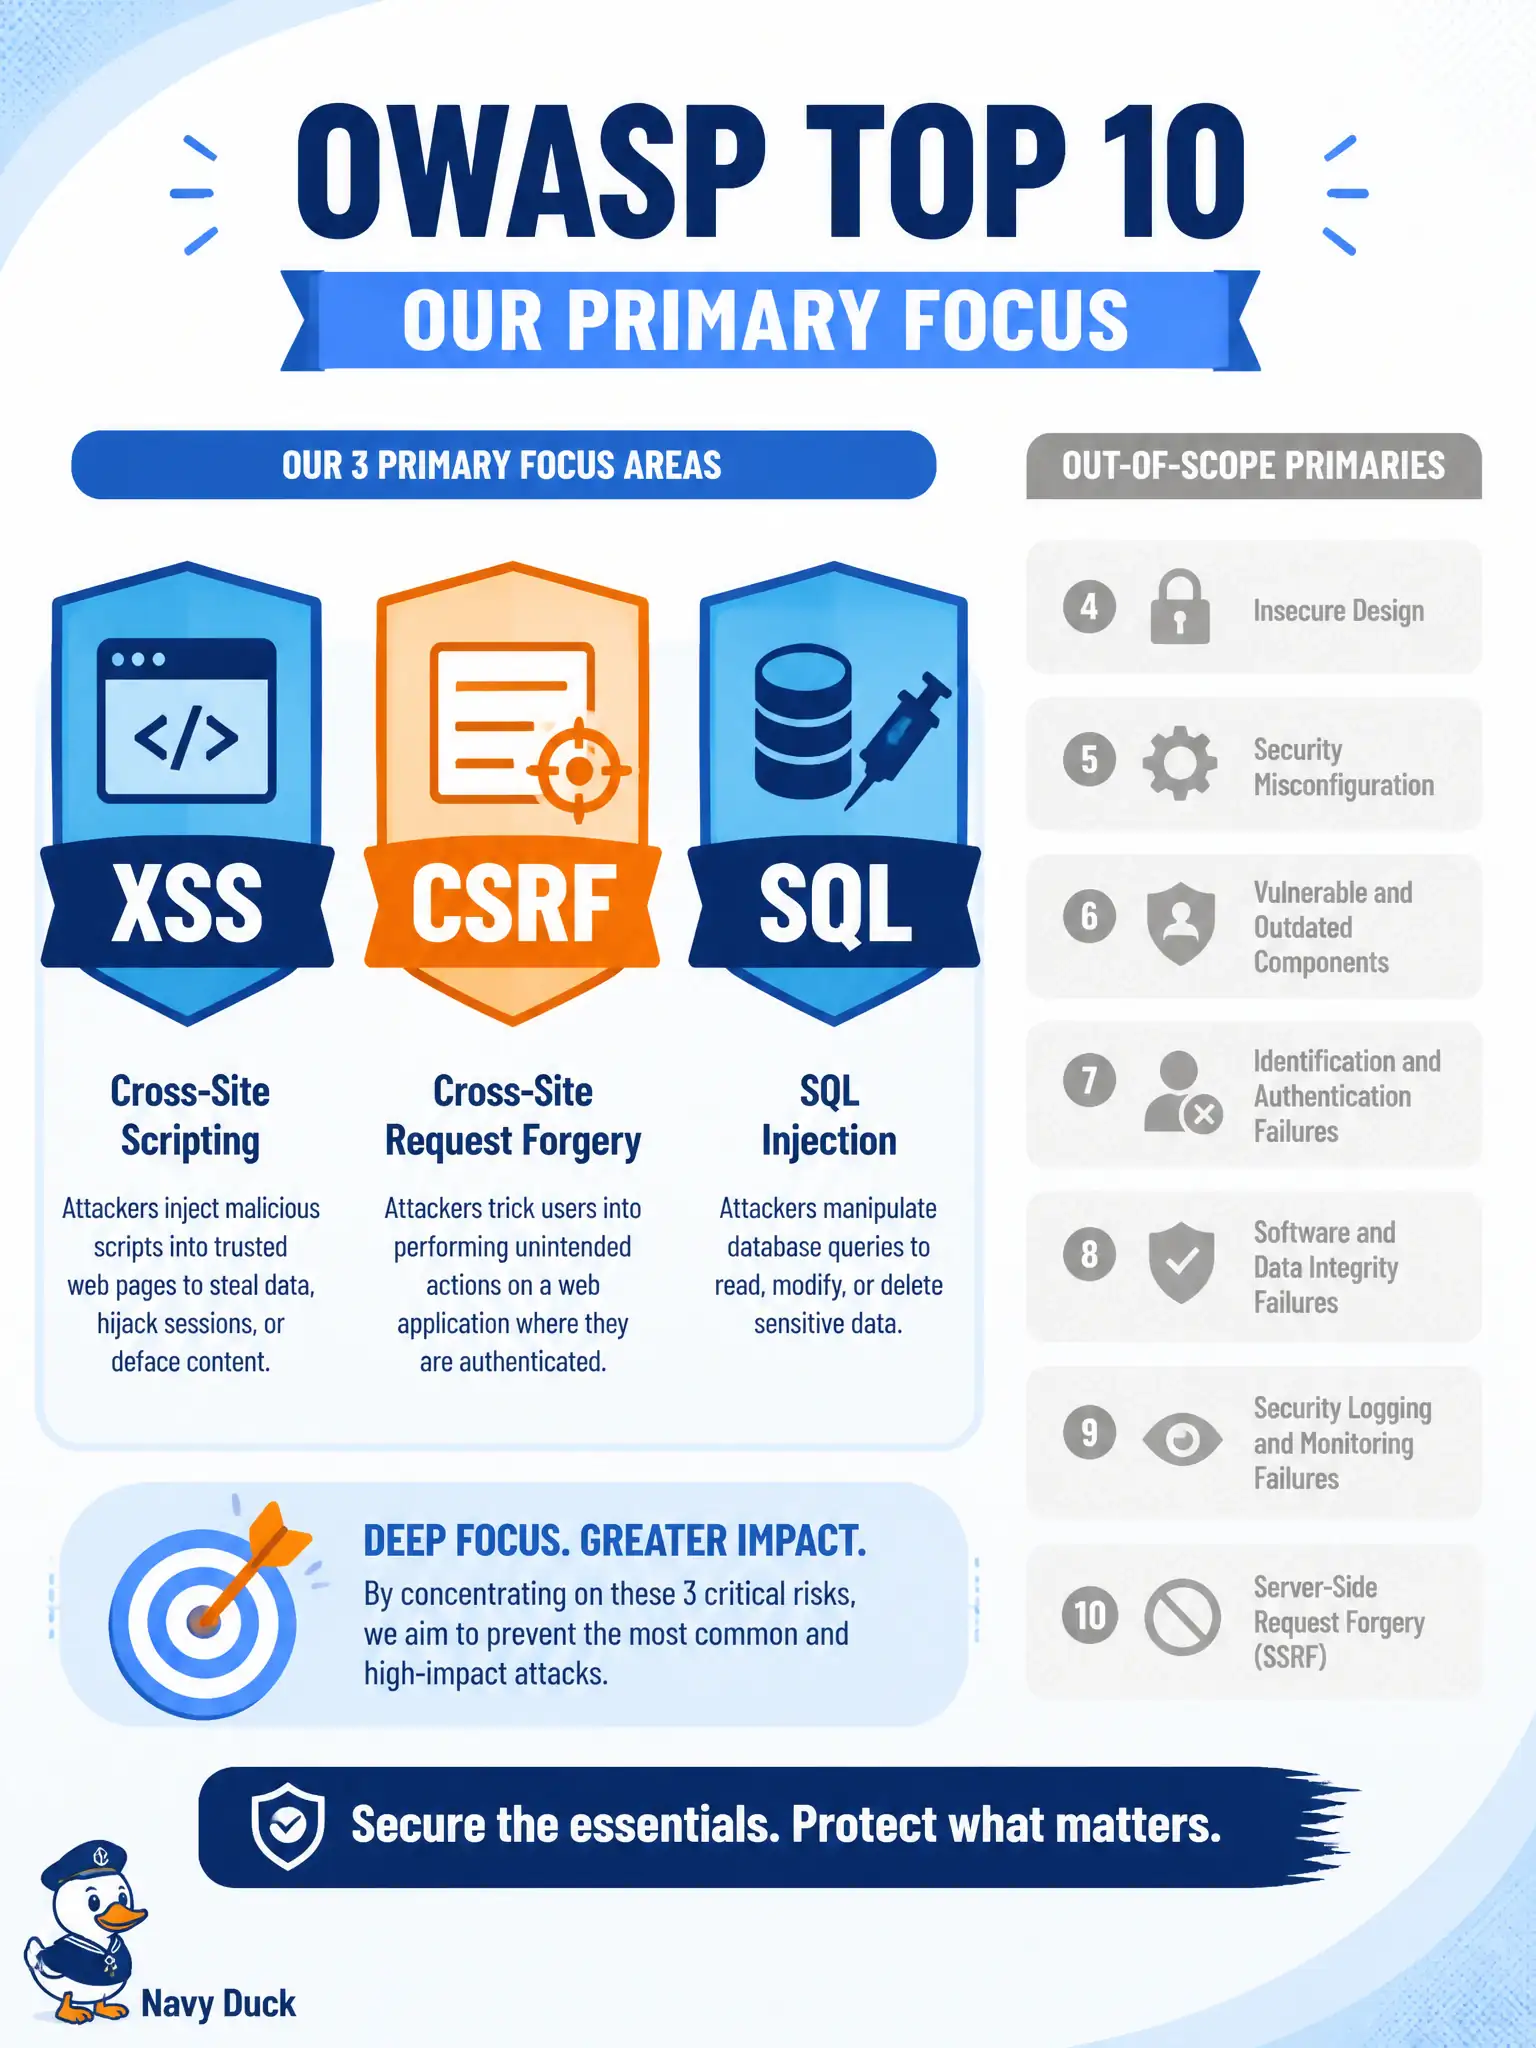
An exam-style lab asks which OWASP threat examples DEVCOR highlights for application mitigation strategies. Which set matches the official named trio?
Select an answer to reveal the explanation.
Short Explanation
Keep the playlist to the three tracks on the syllabus—XSS, CSRF, and SQL injection. Other Top-10 families can distract, but they are not the Domain 4 named trio.
Full Explanation
DEVCOR’s highlighted OWASP threat examples for application mitigation strategies are the classic web trio: cross-site scripting (XSS), cross-site request forgery (CSRF), and SQL injection. Exam items that ask which set matches the official named trio expect exactly those three—and the matching primary mitigations of output encoding, anti-CSRF tokens, and parameterized queries—in a civic or enterprise application context.
SSRF, XXE, and insecure deserialization are important OWASP topics but are not the scored primary trio this bank highlights for the mitigation-strategy items. MACsec downgrade, 802.1X bypass, and IPsec PSK reuse are network-access concerns outside the application OWASP trio. BGP route leak, STP root guard failure, and wireless evil-twin are routing/switching/wireless distractors unrelated to app-layer mitigation strategies on DEVCOR.
Exam caveat: knowing additional OWASP risks is useful operationally, but do not substitute them when the stem asks for the named trio DEVCOR emphasizes. Map each of XSS/CSRF/SQLi to its primary control rather than listing more threats.
Operational check: in study notes, keep a one-line card: XSS→encode, CSRF→token, SQLi→parameters, and verify practice items that name “the trio” match those three spellings.