
The city wants Object Storage buckets for permit PDFs encrypted with a customer-managed Vault master key. How do integrated OCI services use that key?
Select an answer to reveal the explanation.
Short Explanation
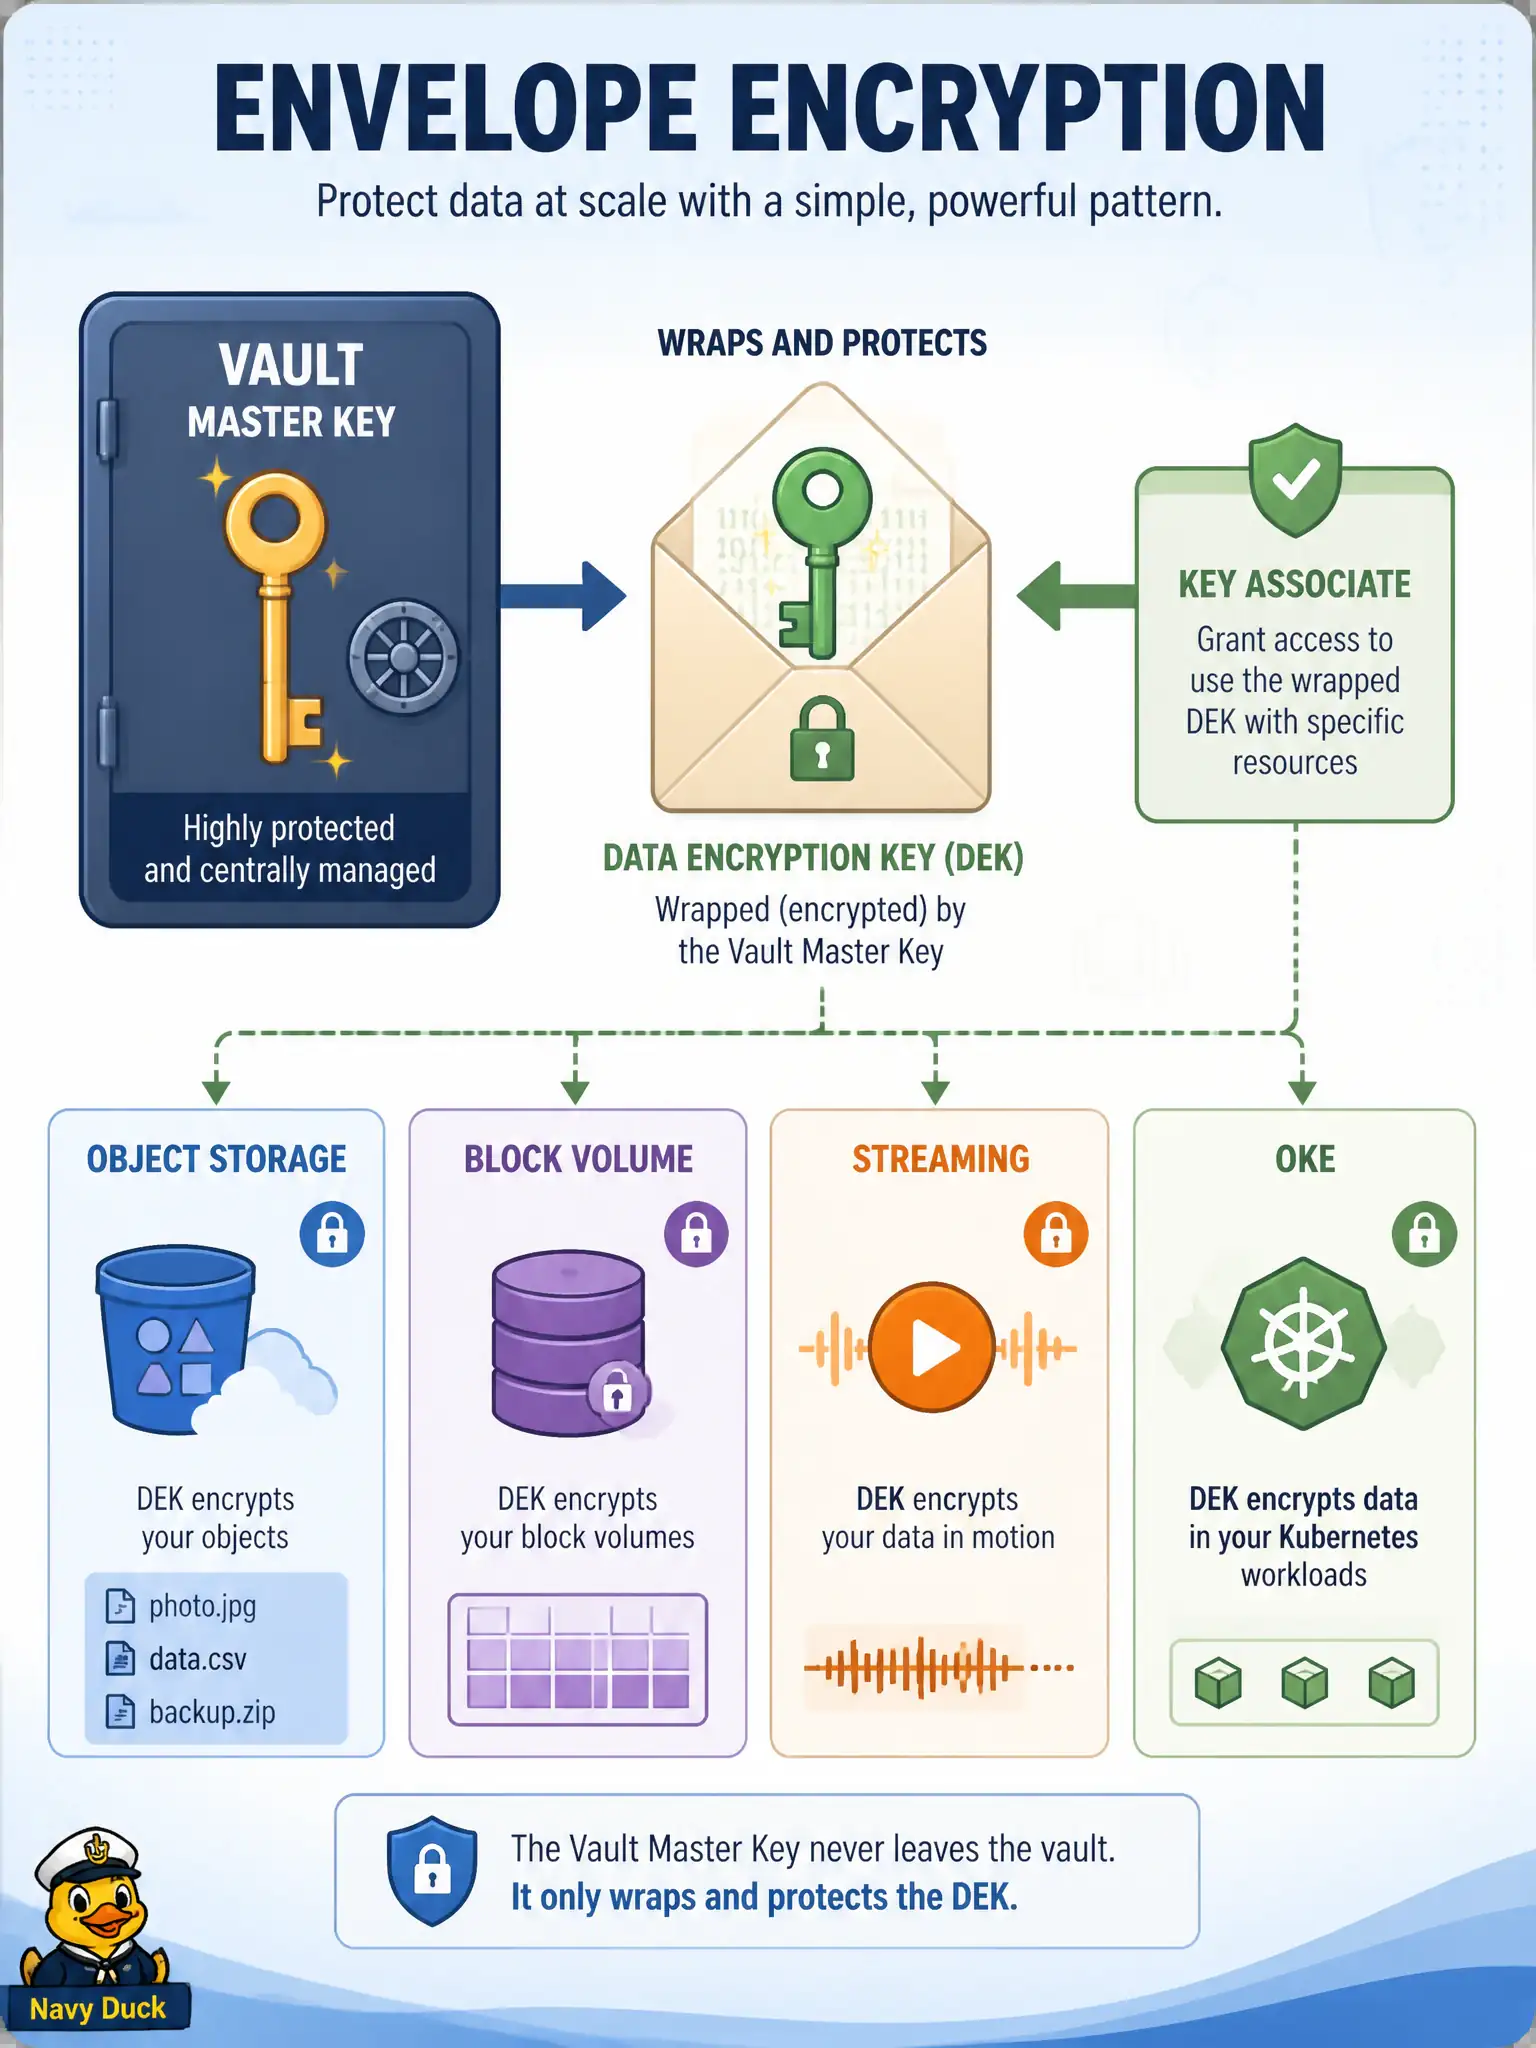
You hand the service a permission slip for your master key; the service asks Vault to wrap and unwrap data keys and never needs you to paste a plaintext DEK into the bucket.
Full Explanation
When Object Storage buckets for permit PDFs use a customer-managed Vault master key, integrated OCI services do not ask developers to paste data keys into bucket metadata. After the tenancy grants the service use of that master key—commonly through key association or key-delegate style rights—Object Storage asks Vault to wrap and unwrap data encryption keys as objects are written and read. The master key stays in Vault; the service performs envelope encryption under that grant. The same pattern applies to other integrated services that support customer-managed keys.
Pasting a plaintext data encryption key into bucket metadata on each upload is operationally unsafe and not how CMK integration works; it would expose DEKs and bypass Vault’s wrap/unwrap path. Turning encryption off on Object Storage whenever a customer-managed key is selected contradicts the goal—CMK replaces or layers on service-managed key control, it does not disable encryption. Claiming only Dedicated KMS HYOK can encrypt Object Storage and that Vault master keys are limited to Functions config is false: Vault master keys are first-class for Object Storage and related integrated services when properly associated.
Exam caveat: associating a key is necessary but not sufficient without IAM that lets the service use the key; missing key-delegate or equivalent rights produces encryption or access failures even when the key OCID is selected on the bucket. Operational check: after associating the municipal master key with the permit-PDF bucket, upload a test object, confirm the bucket shows the customer-managed key, download successfully, and review that unauthorized principals cannot read objects or use the key.