
County library catalog Pods on OKE stay ImagePullBackOff after the Deployment points at a private OCIR repository. What is the most likely missing piece?
Select an answer to reveal the explanation.
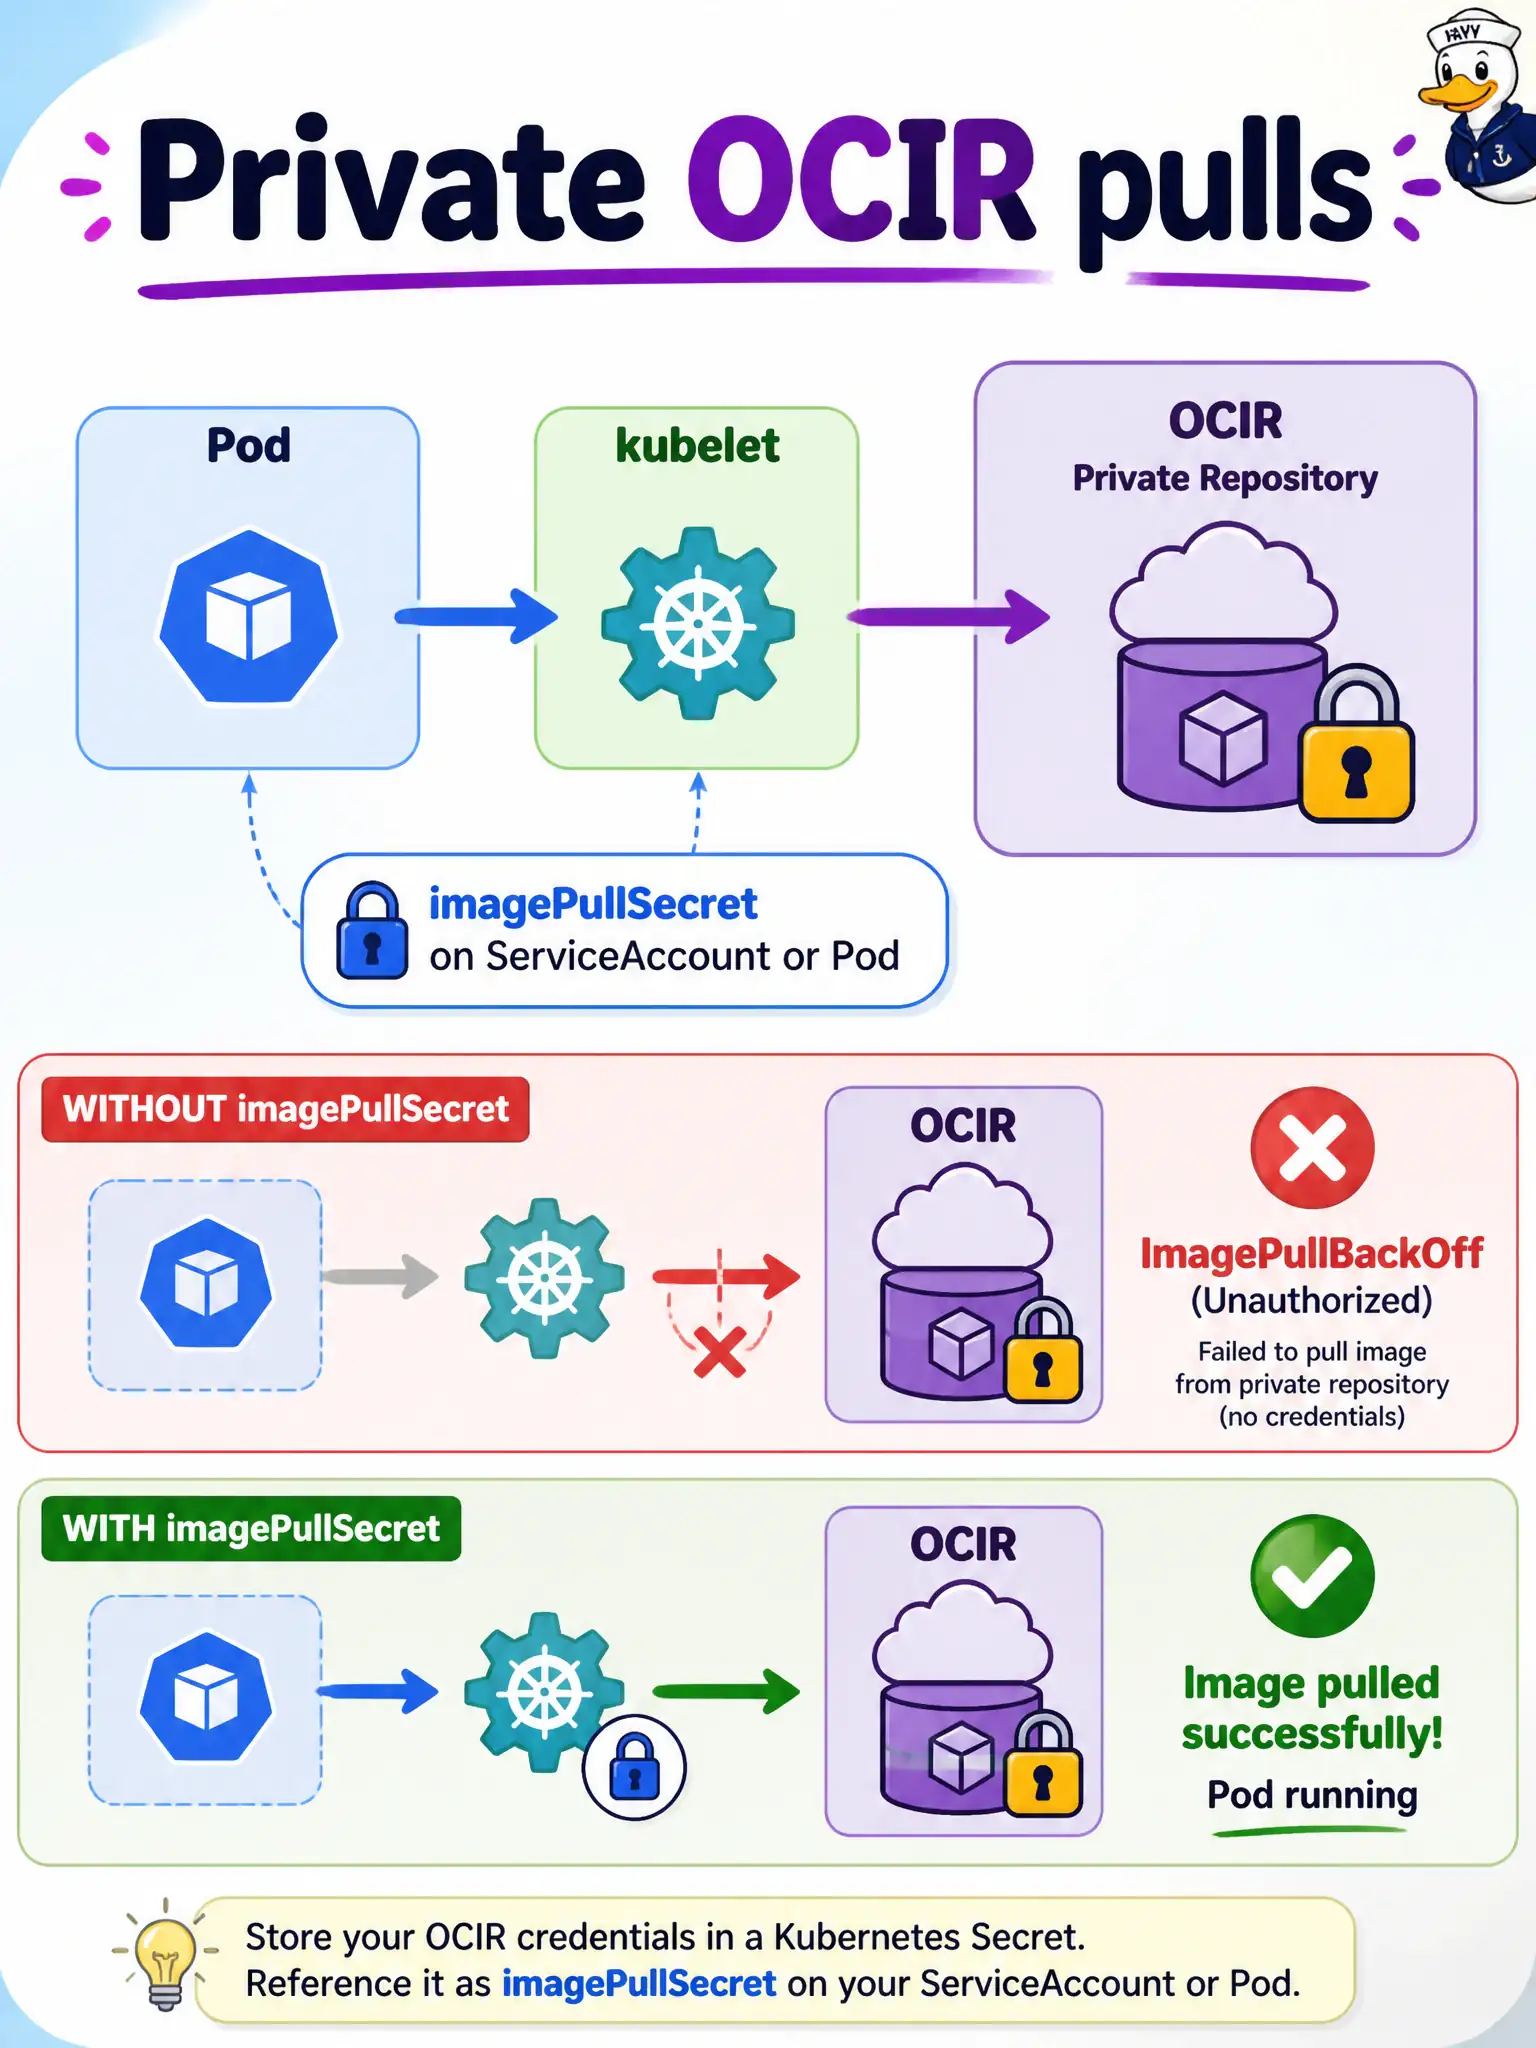
Short Explanation
Private OCIR is a locked staff room; the kubelet needs a badge. That badge is an imagePullSecret on the ServiceAccount or Pod. Public repos do not need it—private ones fail with ImagePullBackOff until credentials are present.
Full Explanation
Private OCIR repositories require authenticated pulls. The missing piece is almost always an imagePullSecret referenced on the Pod or, better, attached to the ServiceAccount the catalog Pods use so every Pod inherits registry credentials. Without that secret, kubelet cannot authenticate to the private repository and containers remain ImagePullBackOff even though the Deployment image field looks correct. Exposing OCIR through a LoadBalancer Service does not fix authentication. A public listener on port 443 might widen network reachability, but private repository pulls still demand registry credentials; publishing the registry endpoint does not substitute for an imagePullSecret and can worsen exposure. A NetworkPolicy that blocks egress is the opposite of what ImagePullBackOff needs. If kubelet or the node cannot reach Object Storage or the registry endpoints, pulls fail harder. Restrictive egress may be useful later for least privilege, but it cannot be the remediation for missing pull credentials. A ConfigMap that merely lists public Docker Hub mirrors does not authenticate to private OCIR. ConfigMaps are not dockerconfigjson pull secrets, and public mirror lists do not carry OCIR auth material for a locked county catalog repository. Exam caveat: imagePullSecrets must be Secrets of the correct dockerconfigjson type in the same namespace as the Pod; referencing a Secret name that exists only in another namespace or storing plain text registry passwords in a ConfigMap still fails pulls. Operational check: describe the failing Pod for ImagePullBackOff events, confirm the ServiceAccount lists the imagePullSecret, verify the Secret contains a valid OCIR auth entry for the repository host, and retry a pull after correcting credentials without changing the application image tag.