
When logging the Docker CLI into OCIR for a non-federated IAM user, what is the correct username shape?
Select an answer to reveal the explanation.
Short Explanation
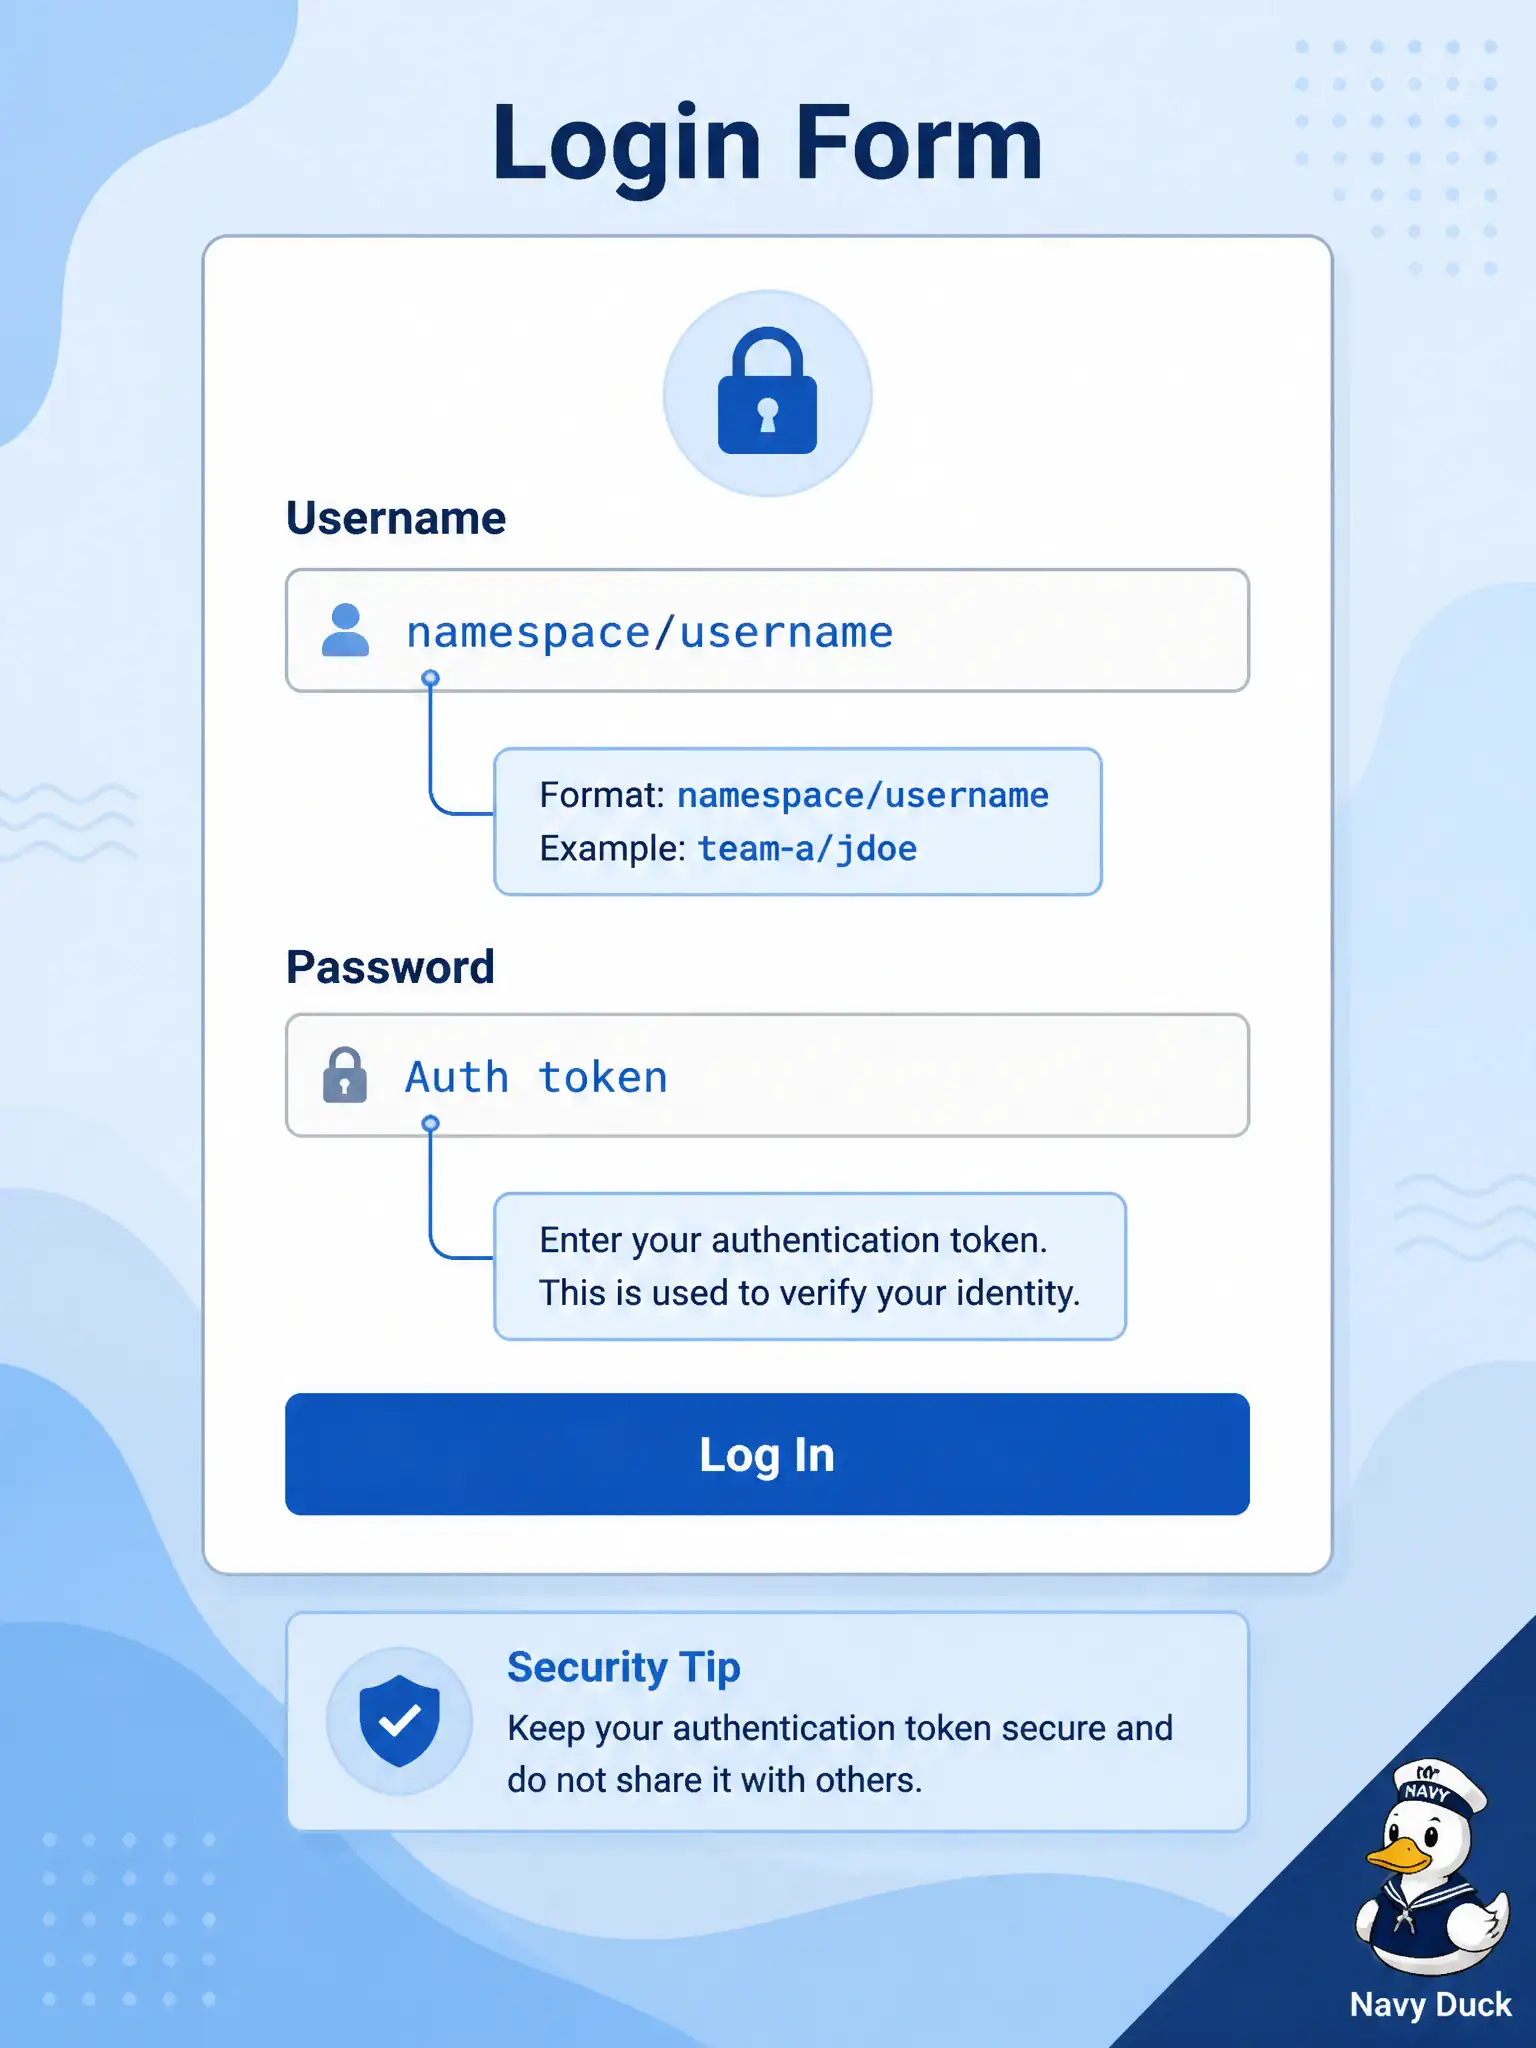
Docker username for OCIR is not the tenancy display name or email alone. It is <tenancy-namespace>/<username>, with the auth token as the password.
Full Explanation
For a non-federated IAM user, the Docker username for OCIR is <tenancy-namespace>/<username>, where tenancy-namespace is the Object Storage namespace string for the tenancy and username is the IAM username. That compound form tells OCIR which tenancy context and which IAM principal the auth token belongs to. Using this shape with an IAM auth token as the password is the documented login pattern for ordinary IAM users.
The tenancy display name alone is not the namespace and omits the user segment, so it cannot identify who is authenticating. The user’s email alone without the tenancy namespace is incomplete for OCIR’s expected username format. Supplying only the IAM user OCID in angle brackets is an OCI resource identifier style, not the Docker username OCIR documents for CLI login.
Exam caveat: federated users need an extra identity-provider segment in the username; applying the simple two-part form to a federated account is a common failure mode covered by related questions. Operational check: open Tenancy Details / Tenancy Information, copy the Object Storage namespace exactly, form <namespace>/<iam-username>, docker login to the regional OCIR host with that username and an auth token, and confirm login succeeds before tagging images.