
When authoring the Dockerfile for a new public-records API, what does the FROM instruction establish?
Select an answer to reveal the explanation.
Short Explanation
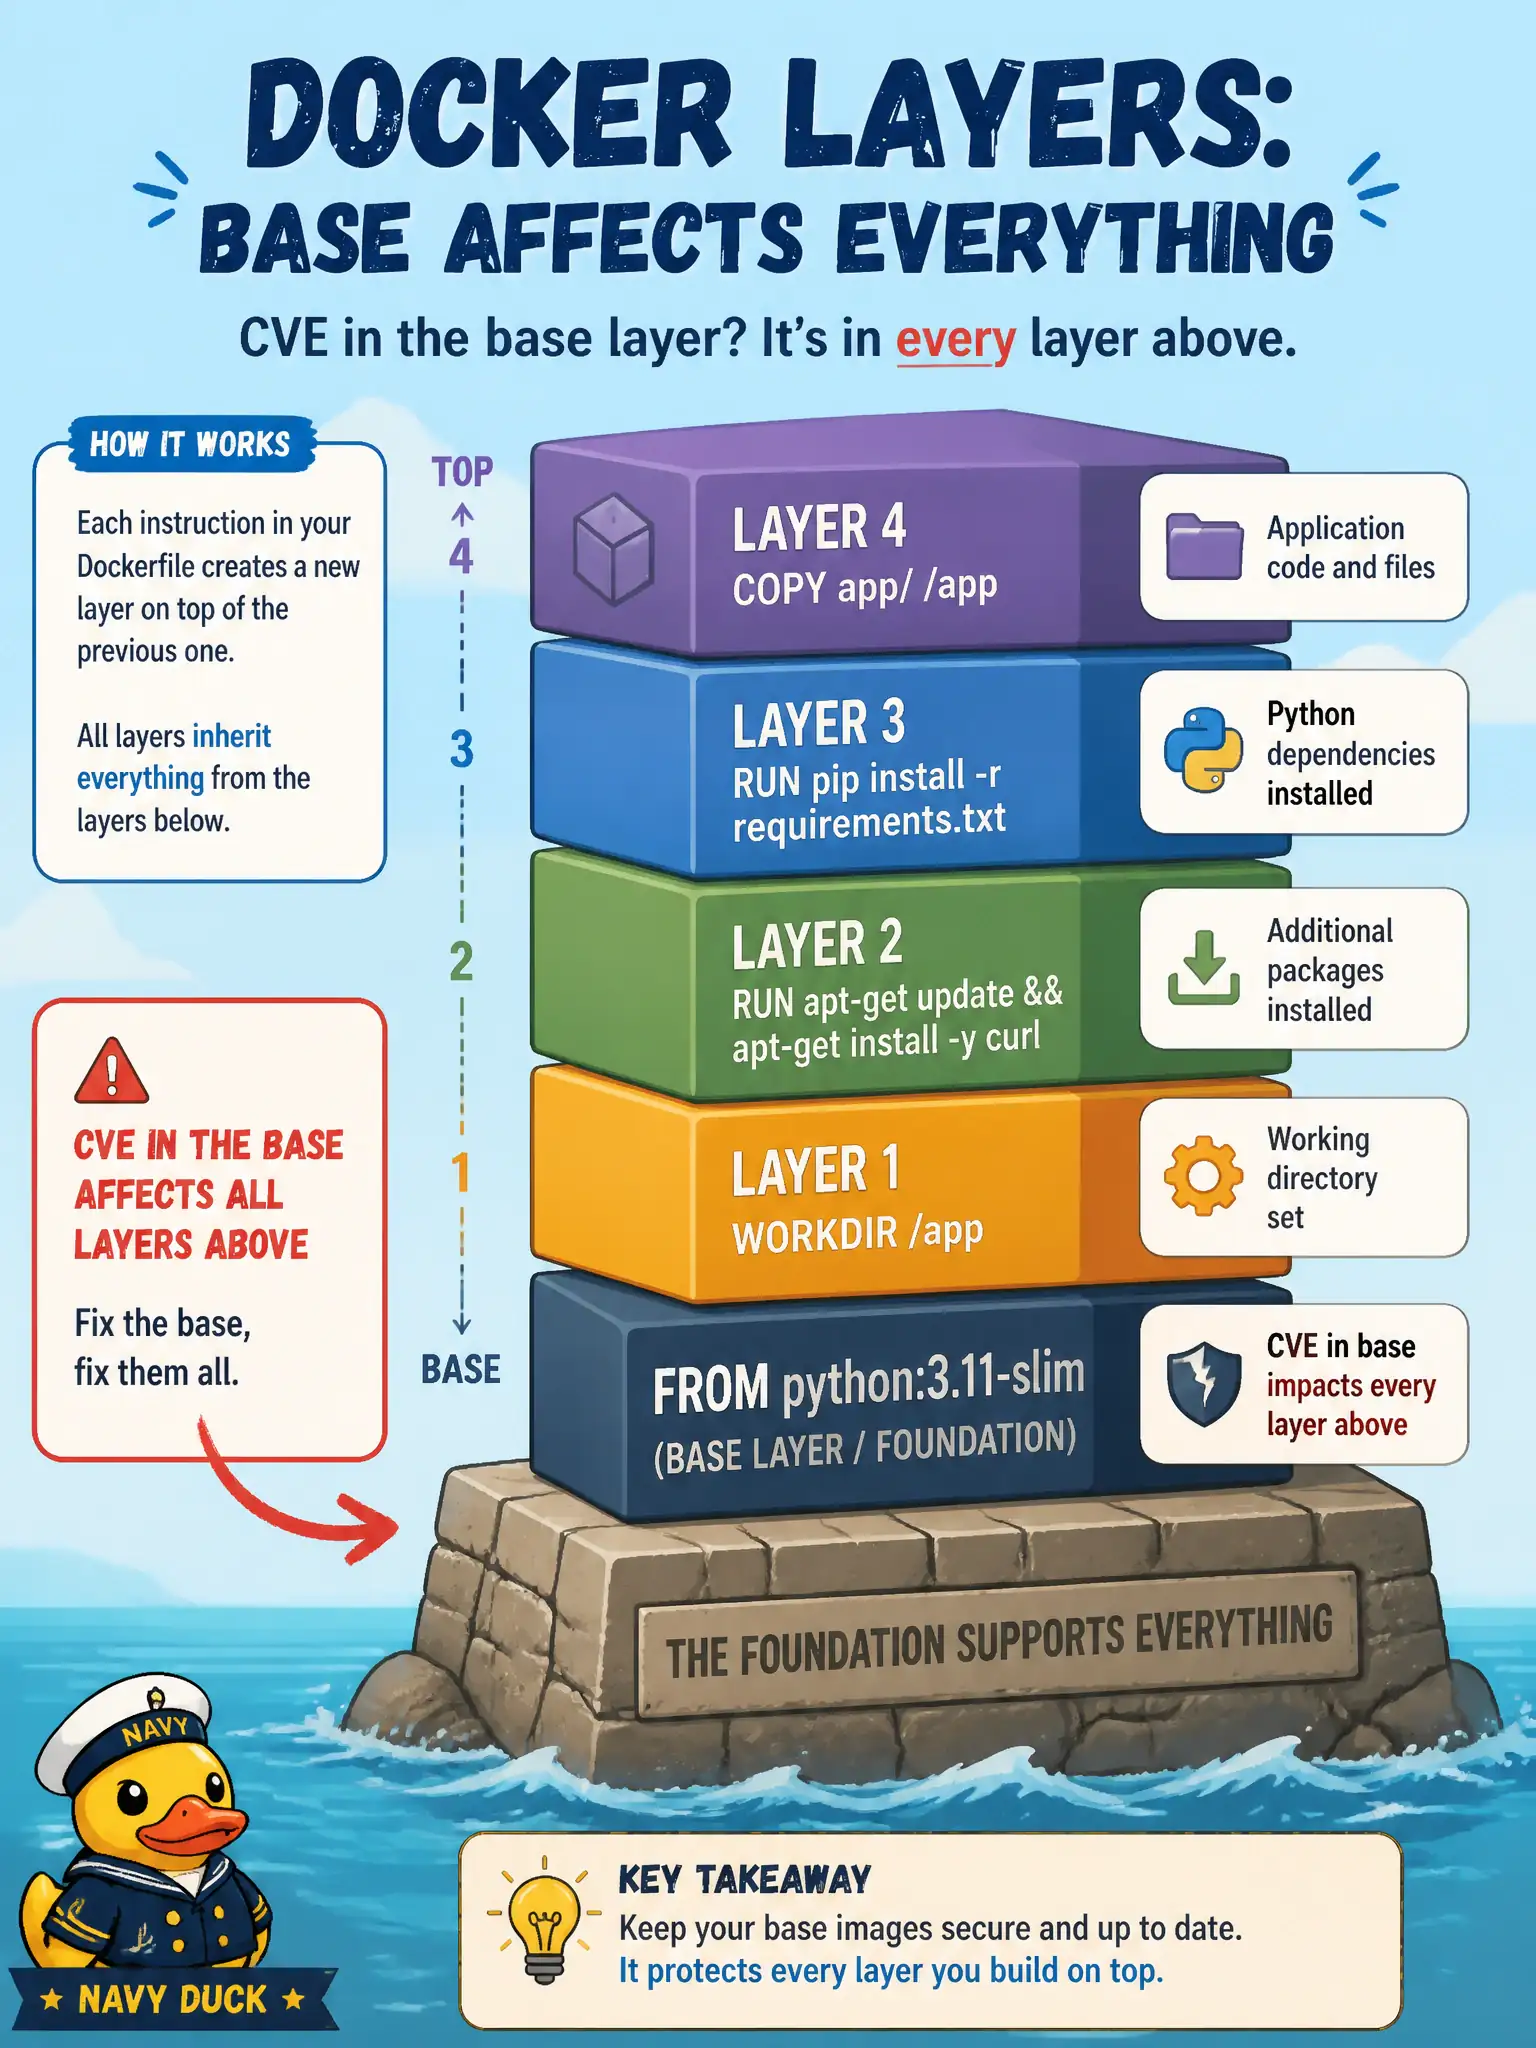
FROM picks the foundation slab under the whole building. Everything you add later sits on that base—so a neglected or bloated base becomes everyone’s problem.
Full Explanation
FROM names the starting image—the base filesystem and runtime—that every later instruction for the public-records API stacks onto. That single line decides which packages exist by default, which language runtime is present, how large the early layers are, what default user the base assumes, and how quickly upstream CVEs appear in every downstream municipal build. Treat base selection as a deliberate foundation decision, not an afterthought or a popularity contest among Linux distros.
FROM does not configure the Kubernetes Service port that will publish the container; publishing is cluster networking decided later with Services and related objects. It does not declare an OCI Vault secret the process will fetch at runtime; secrets belong outside image layers and build context. It is not the registry credential allowed for later docker push; registry authentication is a client and daemon concern at publish time, separate from the recipe’s first instruction.
Exam caveat: a bloated or neglected base becomes everyone’s problem across every rebuild—prefer minimal or purpose-built bases for production APIs and pin base digests when reproducibility and audit matter. Operational check: after choosing FROM, record the resolved base digest in the build log, vulnerability-scan the resulting image, and track which upstream CVEs travel with every public-records rebuild so the team can rotate bases on purpose.